AI AGENT SECURITY

AI agents act.
You stay in control.

Secure and govern your AI agents. Assess risks, define permissions and approval rules, and keep a verifiable record of policy decisions.

FIRSTCVE Program
Conference co-hosts

VulnCon 2027

Our founder joins the
Program Committee.

NVIDIA Inception Program

NVIDIA Inception

Oktsec joins NVIDIA’s
startup program.

SECURITY INTELLIGENCE

Radar

Know what matters.
Act with context.

Security incidents, vulnerabilities and practical guidance to help your team decide what needs attention.

Explore Radar
Incident analysisAct now
Danfoss / Copeland / Dixell

Cold chain attacks: protect refrigeration controls and monitoring

Evidence
Incident documented by multiple sources

Recommended action

Remove public administration access. Verify safe setpoints, actual temperatures and alert delivery with operations; secure maintenance access and plan recovery for the exact equipment.
Security advisoryAct now
BeyondTrust

BeyondTrust Remote Support: exploited appliance flaw

CVE-2026-102764
Evidence
Attacks confirmed

Recommended action

Apply BT26-05-RS or upgrade Remote Support to 26.3.1 or later; investigate unexpected appliance activity.

RECOGNITION · ACE BARRANQUILLA 2026

Partnership
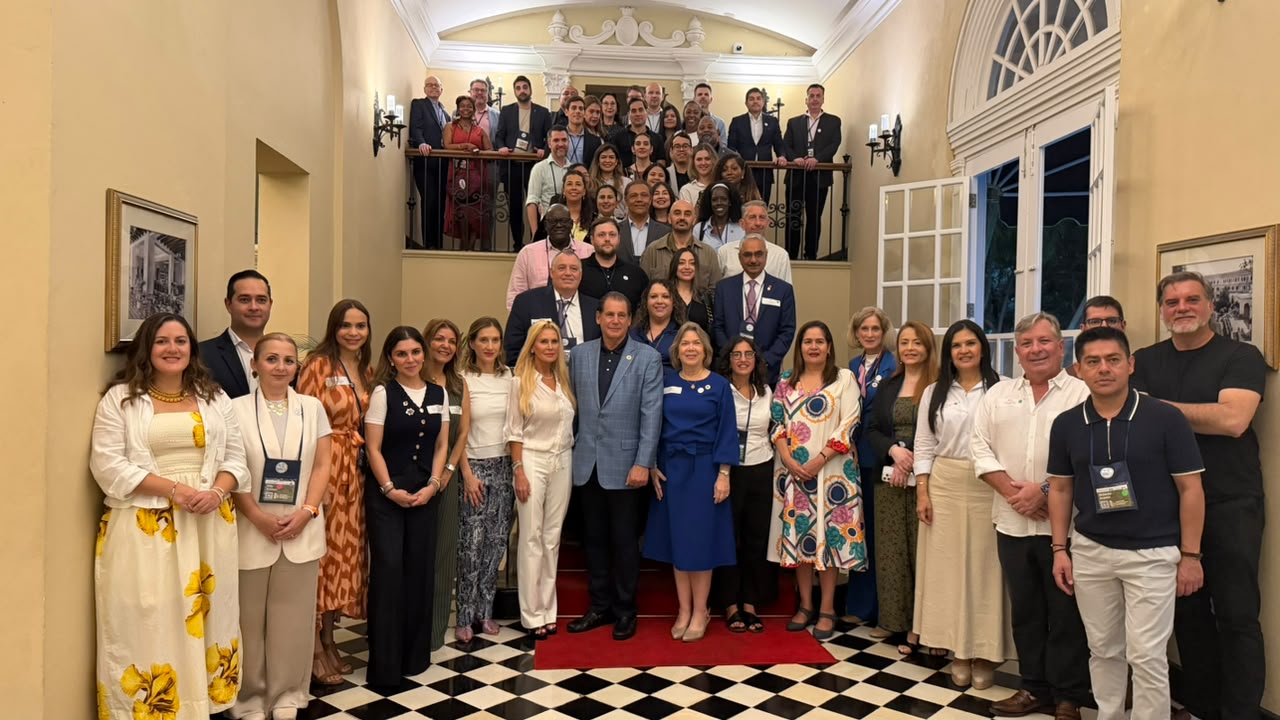
Catalyst Award.

Oktsec founder Gustavo Aragón received the award from Leandro Rizzuto, U.S. Ambassador to the Organization of American States (OAS), during ACE Barranquilla.

Read the award story
Participants at ACE Barranquilla 2026
ACE Barranquilla 2026 · Photograph provided by Gustavo Aragón
WORK WITH OKTSEC

Where does your
team need to start?

Evaluate a system, put controls around an AI pilot or help your team build the skills to move forward.

01
ASSESSMENT & PENTESTING

Assess your systems.

Test AI agents, web applications and APIs within an agreed scope. Get reproducible findings and recommended fixes.

A defined scope. Findings your engineers can use.

Scope an assessment
02
AI GOVERNANCE & PILOTS

Plan an AI pilot.

Set permissions, assign reviewers and define evaluation criteria for an AI workflow. Put these governance decisions into practice in a scoped pilot.

One workflow. Clear responsibilities and criteria.

Discuss a pilot
03
TRAINING & TALKS

Prepare your team.

Talks, workshops and training programs for companies, governments and universities. Work through AI risks and practical security decisions.

For technical teams and people getting started.

Explore training
THE OKTSEC PLATFORM

AI governance.
From policy to action.

Define who is responsible for an agent, what it can access and which actions need approval.
Test those controls and keep evidence your team can review.

Explore AI agent governance
oktsecControl / How it connects
WORKFLOW OVERVIEW

Policy in effect

coding-workflow
  1. 01
    DEFINE THE SCOPEDefine permitted tools and destinations
  2. 02
    APPLY THE CONTROLEnforce inside your environment
  3. 03
    REVIEW THE RESULTVerify the evidence independently
Signed policy · Applied locallyOKT / 001
Explicit authority. A verifiable decision.

Apply explicit policy where agents act. Allow approved work, hold exceptions for review and keep a record of every decision.

Explore Control

PUT IT INTO PRACTICE

Plan the next step.

Choose where to run Oktsec, connect controls to your governance requirements and explore workflows for your team.

LATEST RESEARCH

Read the research.
Explore the tools.

All research

Explore Aguara and the open-source projects behind our work.

Open-source projects
BEFORE YOU GET STARTED

Deployment and
security questions.

How requests are checked, where oktsec runs and how to verify the audit trail.

Explore deployment
01

Where does oktsec run?

At the points between an agent and the tools or systems it can access. Depending on the workflow, that can be a local MCP proxy, a gateway or an HTTP service. Actions routed through oktsec are checked before they proceed.

02

Does an LLM make the security decision?

No. The enforcement pipeline is deterministic. It evaluates identity, permissions and content against configured policy. A model does not decide whether an action is authorized.

03

Do we need to replace our agent tools?

You can keep your agent clients and MCP servers. Oktsec can wrap MCP server connections or sit in the request path as a gateway. The initial assessment identifies where the control belongs in your workflow.

04

What happens when an action breaks policy?

Depending on the policy and severity, oktsec can flag and log the request, quarantine it for human review or block it. The audit record connects the request to the decision and the rules involved.

05

When should we review agent permissions?

Review permissions when you add a tool or connector, change credentials or expand a task. Check the new access paths and test which actions can run without approval. A previous assessment covers the configuration tested at that time.

06

Can we verify evidence independently?

Yes. Audit records form a tamper-evident hash chain. When a node key is configured, records are also signed and can be verified offline with the public key.

07

What should we start with?

Choose one workflow that touches code, tools, credentials or infrastructure. Define its scope, test the execution path and use the findings to decide where to apply control.

WORK WITH OKTSEC

Find your security gaps.
Build a plan to close them.

Pentesting, AI security and governance, and practical training. Work directly with our team to define the scope, priorities and next steps.